
Under INTERPOL’s coordination, investigators from participating countries joined forces in Operation Serengeti III between 29 June and 31 August 2026 to combat cyber-enabled fraud, ransomware, business email compromise (BEC), online scams and digital extortion.
Authorities identified 65,929 victims targeted by cyber criminal networks, underscoring the scale and sophistication of today’s digital threats. Financial investigations linked criminal activity to losses exceeding USD 385 million.
Cyber threat landscape
The operation comes as INTERPOL’s African Cyber Threat Assessment Report 2026 points to a rapidly evolving threat landscape, with artificial intelligence increasingly enabling cybercrime activity across the continent and cyber-enabled financial losses continuing to rise.
Prior to the operation, investigators from 20 African countries and from the United States were provided with actionable intelligence on suspicious domains, IP addresses and command-and-control infrastructure linked to criminal activity.
Operation Serengeti III was supported by private-sector partners to disrupt cyber criminal networks operating across Africa. They provided critical intelligence, technical analysis and operational expertise, helping authorities identify targets, map criminal networks, and support investigative activities across the region.
INTERPOL’s Director of Cybercrime Neal Jetton said:
“Cybercrime networks operate without regard for borders, exploiting technology to target victims on an unprecedented scale.
“Operation Serengeti III reinforces a clear message: while cybercrime is increasingly borderless, international cooperation remains one of the most effective tools for disrupting criminal networks, recovering criminal assets and protecting communities from digital harm.”
Operational highlights
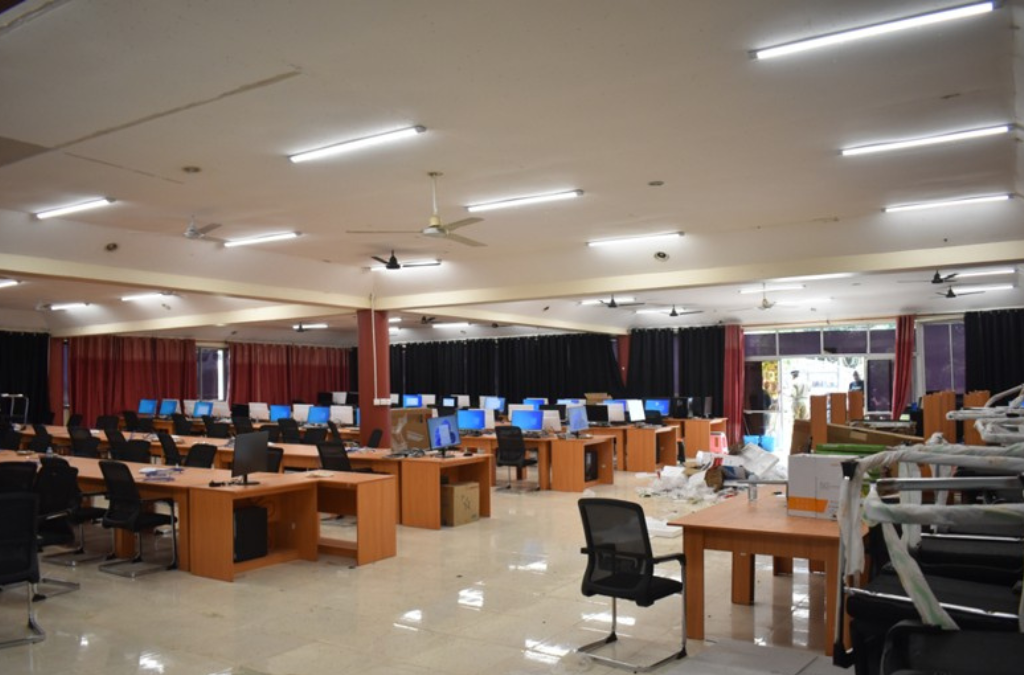
In Uganda, authorities dismantled two transnational fraud rings and arrested 365 foreign nationals linked to sophisticated online investment and pension fraud schemes targeting victims across Asia. Investigators uncovered a rotating call-centre model using scripted communications, fake trading platforms and fraudulent websites to deceive pensioners into investing in non-existent opportunities.
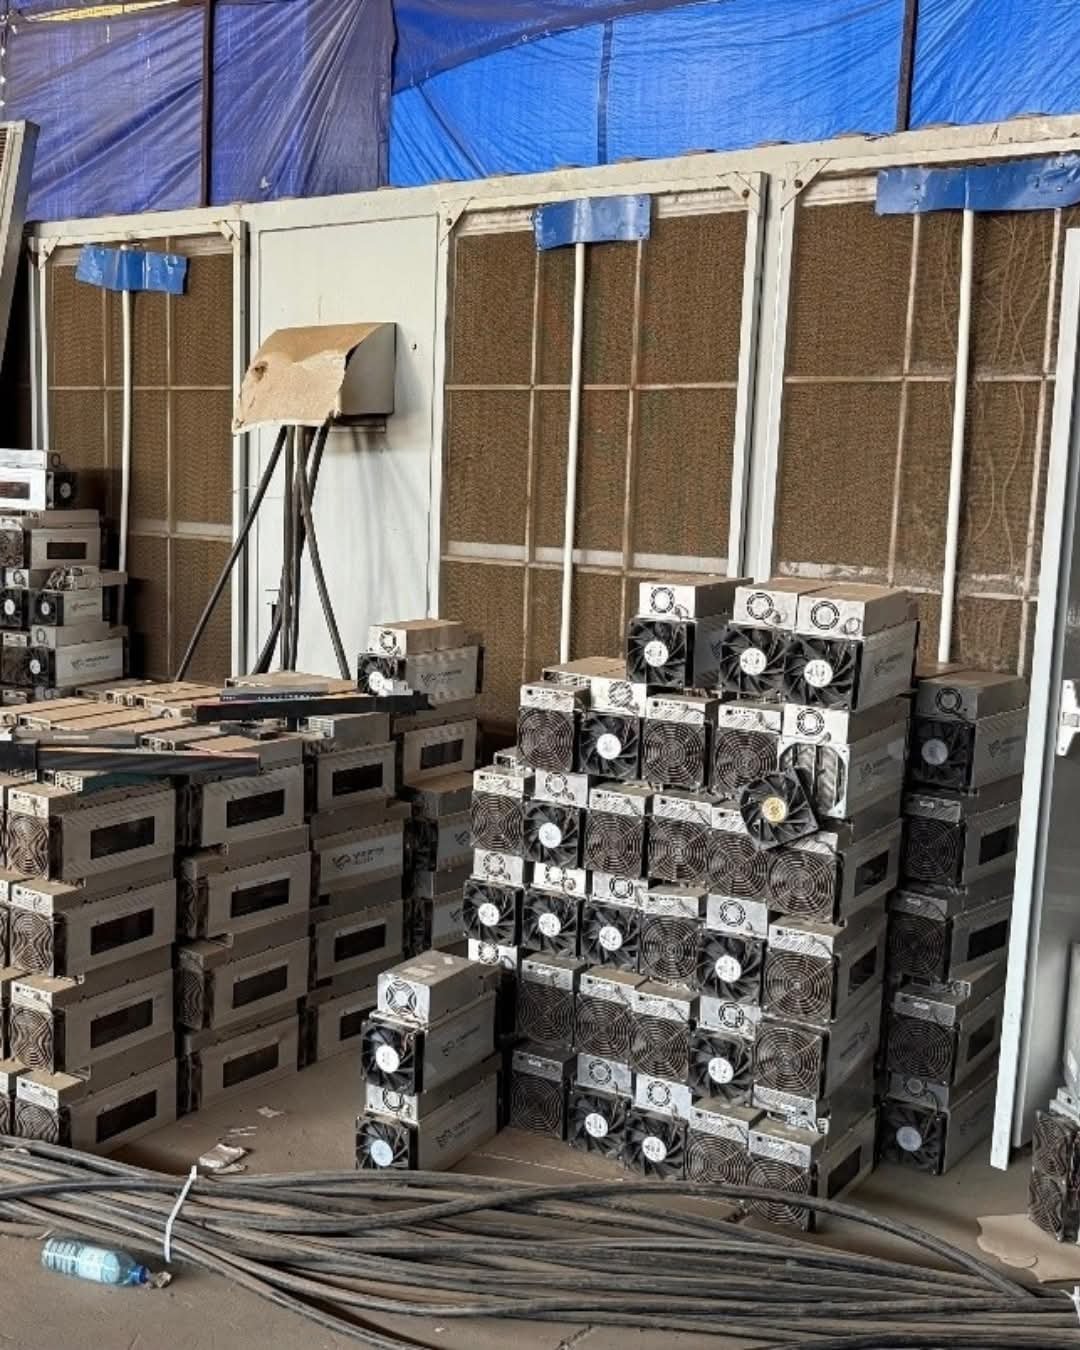
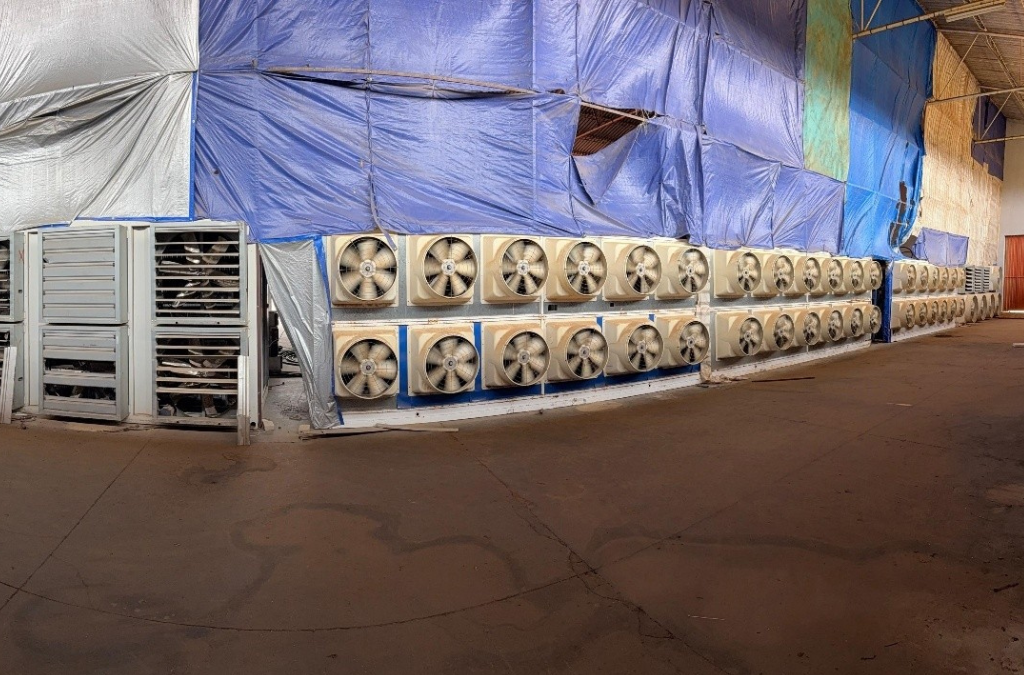
In Angola, investigators dismantled two illegal cryptocurrency mining centres, arresting nine suspects and seizing more than 2,000 cryptocurrency mining devices alongside six illegal power transformation stations. The seized electrical infrastructure alone was valued at more than USD 1 million.
In Nigeria, authorities arrested a suspect behind a large-scale phishing and business email compromise operation that harvested software credentials and amassed approximately 2.1 million email addresses. Investigators also recovered a luxury vehicle suspected to have been purchased with criminal proceeds.
A separate Nigerian investigation targeted an international investment fraud scheme promoted via messaging apps, leading to the arrest of a suspect. Financial investigations revealed the movement of more than USD 2.4 million in suspected criminal proceeds, much of which was laundered through cryptocurrency transactions.
Elsewhere, authorities dismantled a malicious mobile loan application scheme in Tanzania, disrupted a social media-based vehicle import fraud network in Gabon, and arrested 30 suspects linked to a cybercrime operation in the Republic of Congo.
Several investigations stemming from Operation Serengeti III remain active, with authorities continuing efforts to identify additional suspects, trace illicit proceeds and analyze digital evidence seized during the operation.
Operation Serengeti III was supported by partners which included Group-IB, Kaspersky, Fortinet, TrendAI, Team Cymru, Uppsala Security, Cybercrime Atlas, Meta, the Global Anti-Scam Alliance and the Postal and Telecommunications Regulatory Authority of Zimbabwe.
The operation was co-funded by the Global Action on Cybercrime Enhanced (GLACY-e) project, a joint initiative of the European Union and the Council of Europe.


